SECTORA Cybersecurity Software
Testnet Live monitoring Post-quantum ← Main site

Cybersecurity Software · §11

The security engine
beneath every product.

Sectora Shield is the quantum-resistant cybersecurity layer that protects custody, trading and live data across the entire Sectora network — the same engine that secures the DEX, the hash market and the dashboard's on-chain feeds.

Threats blocked0Since page load
Products protected7Across the network
Custody integrity100.000%Records verified
Engine uptime100.00%Testnet to date

Incident files · 2026

The year's biggest attacks, and how Shield breaks the chain

Four short analyses. Incidents as reported publicly; Shield outcomes are illustrative scenarios on testnet.
Incident analysis · Bitget · Sep 24, 2026

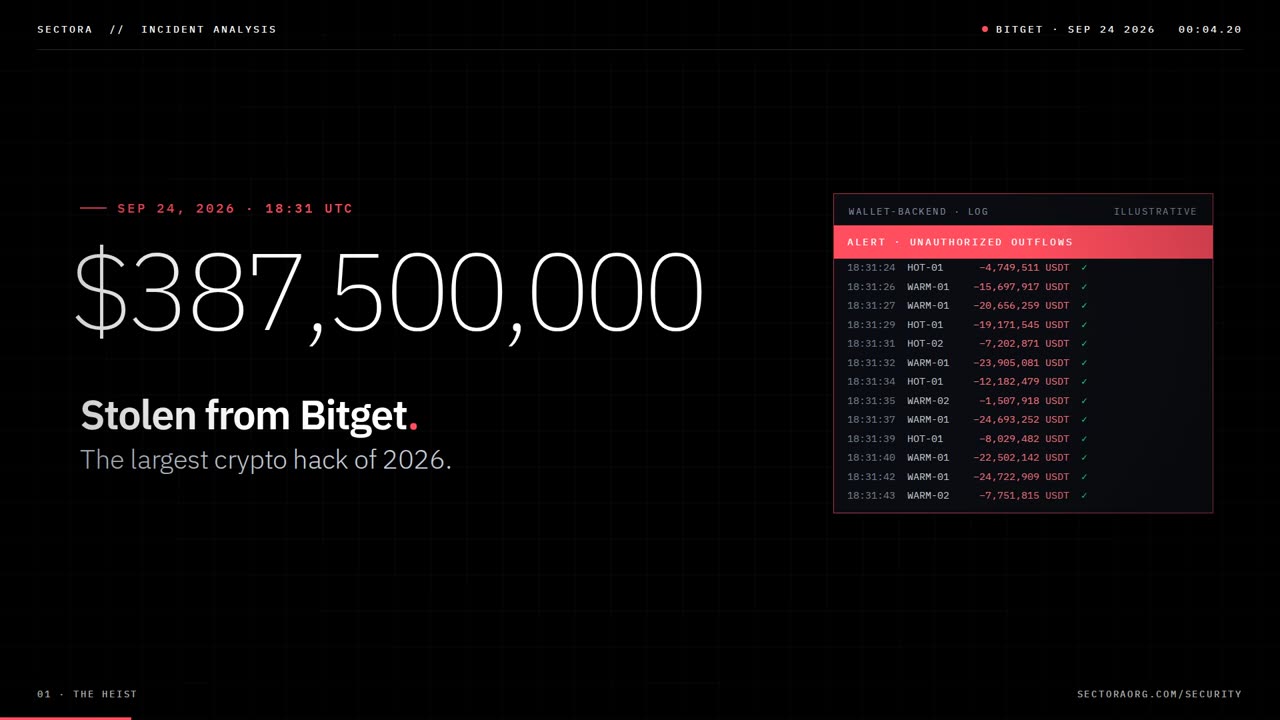
$387.5M walked out. No private key was stolen.

Twenty-five days inside, unseen. A zero-day in a third-party security product opened the door; a database password stored in an environment variable did the rest. The attackers moved laterally into the wallet infrastructure, spoofed transaction data in the backend, and Bitget's own system authorized and signed. The signatures were valid: the system signed whatever it was told.

$387.5MStolen
25Days inside
$1.1MFrozen

How Shield breaks the chain. Orders signed at origin with ML-DSA, an integrity ledger that re-checks every custody record, channels that need an ML-KEM identity, and on-chain monitoring that pauses abnormal outflows. Verify before you sign.
Comparison · same attack

Same attack. Two endings.

The Bitget attack chain replayed step by step, without Sectora Shield and with it: access granted or contained, 25 days unseen or flagged, signed or rejected, −$387.5M or $0 moved.

Illustrative scenario
Threat intelligence · 2026

Four attacks, one pattern. Then quantum.

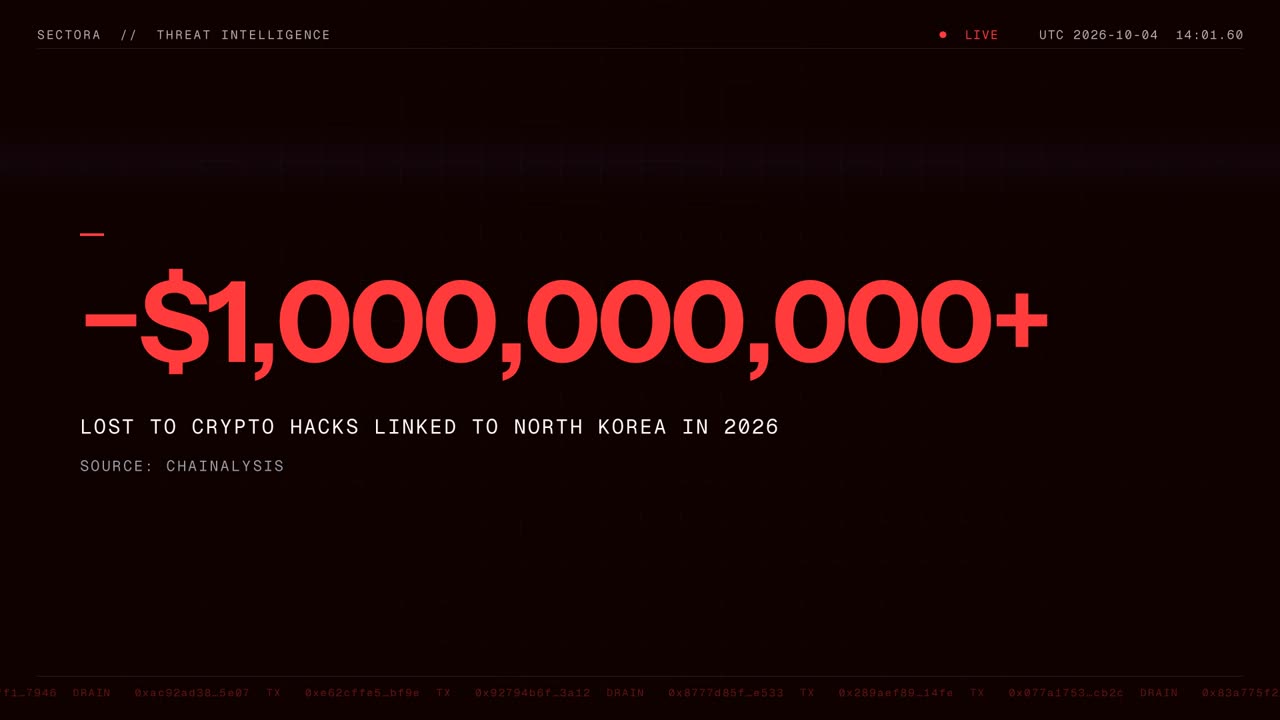
More than $1B lost to crypto hacks linked to North Korea in 2026 (Chainalysis). KelpDAO's cross-chain bridge drained of $136.5M; a validator software bug on Liquid Network let attackers mint unbacked bitcoin. Next: a quantum computer could break ECDSA, the signature scheme behind Bitcoin and Ethereum wallets.

Post-quantum · threat model

Stolen today. Unreadable tomorrow.

Harvest now, decrypt later: encrypted traffic, custody records and public keys are intercepted today and stored for years, waiting for a quantum computer to break RSA and elliptic-curve keys. Shield wraps the same data in NIST's post-quantum standards, so what is stolen stays unreadable.

Live threat monitor

Simulated preview feed — testnet traffic, illustrative of the engine's detection surface

What Shield protects

One engine, applied at every layer of the network

Built on standardized post-quantum cryptography

NIST finalized these algorithm families in 2024 (FIPS 203/204/205) — Shield is built on that same foundation
FIPS 203 · ML-KEM

Key encapsulation

Lattice-based key exchange (CRYSTALS-Kyber family) secures every session and message between validators, custody records and the network's live data feeds.

FIPS 204 · ML-DSA

Digital signatures

Lattice-based signatures (CRYSTALS-Dilithium family) authenticate custody transfers and validator actions — built to remain unforgeable even against quantum attacks.

FIPS 205 · SLH-DSA

Hash-based signatures

A stateless hash-based signature scheme (SPHINCS+ family) backs long-horizon custody records — the class of asset that has to stay verifiable for decades.

Why this matters for tokenized assets

Custody records for real-world assets have to stay valid for as long as the property does — often decades
Classical encryption (e.g. RSA-2048)
Not quantum-resistant
Sectora Shield post-quantum stack
Built for the post-quantum transition

Illustrative comparison, not a benchmark. NIST recommends migrating long-lived records to standardized post-quantum algorithms ahead of any cryptographically-relevant quantum computer — Shield is built on that guidance from day one.

Integrity ledger

Every custody record is checked against tampering on a continuous loop

Built to be shared

Available beyond Sectora

Post-quantum cryptography is moving from research to requirement industry-wide — firms like IBM, Google and Microsoft are already investing in it for their own infrastructure. Sectora Shield is built to be licensed the same way: technology companies and high-level cryptographic projects can adopt this class of protection without building it from scratch — a security engine as a second product line alongside the network itself.

Request enterprise access